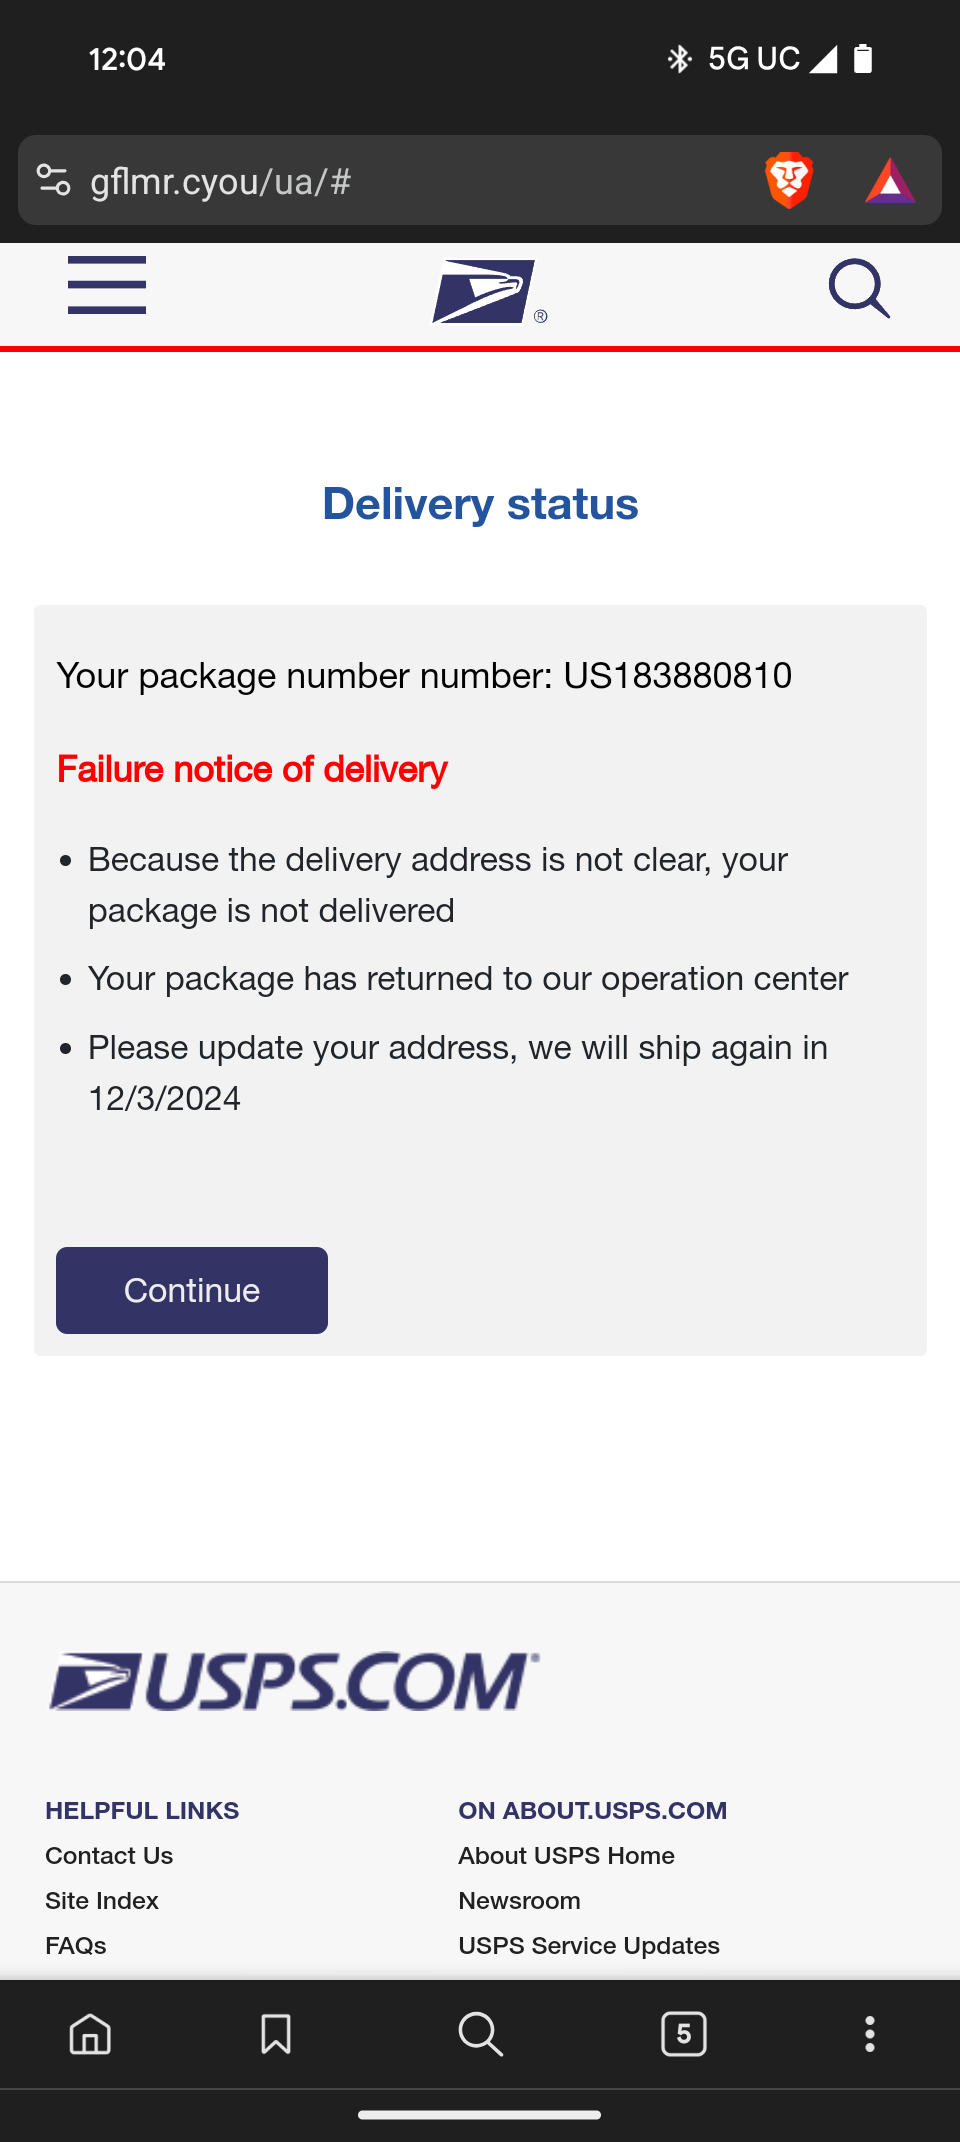
Url looks suss. Seems kinda sophisticated for the usual ups fishing scam. Here’s the text message I got leading here.
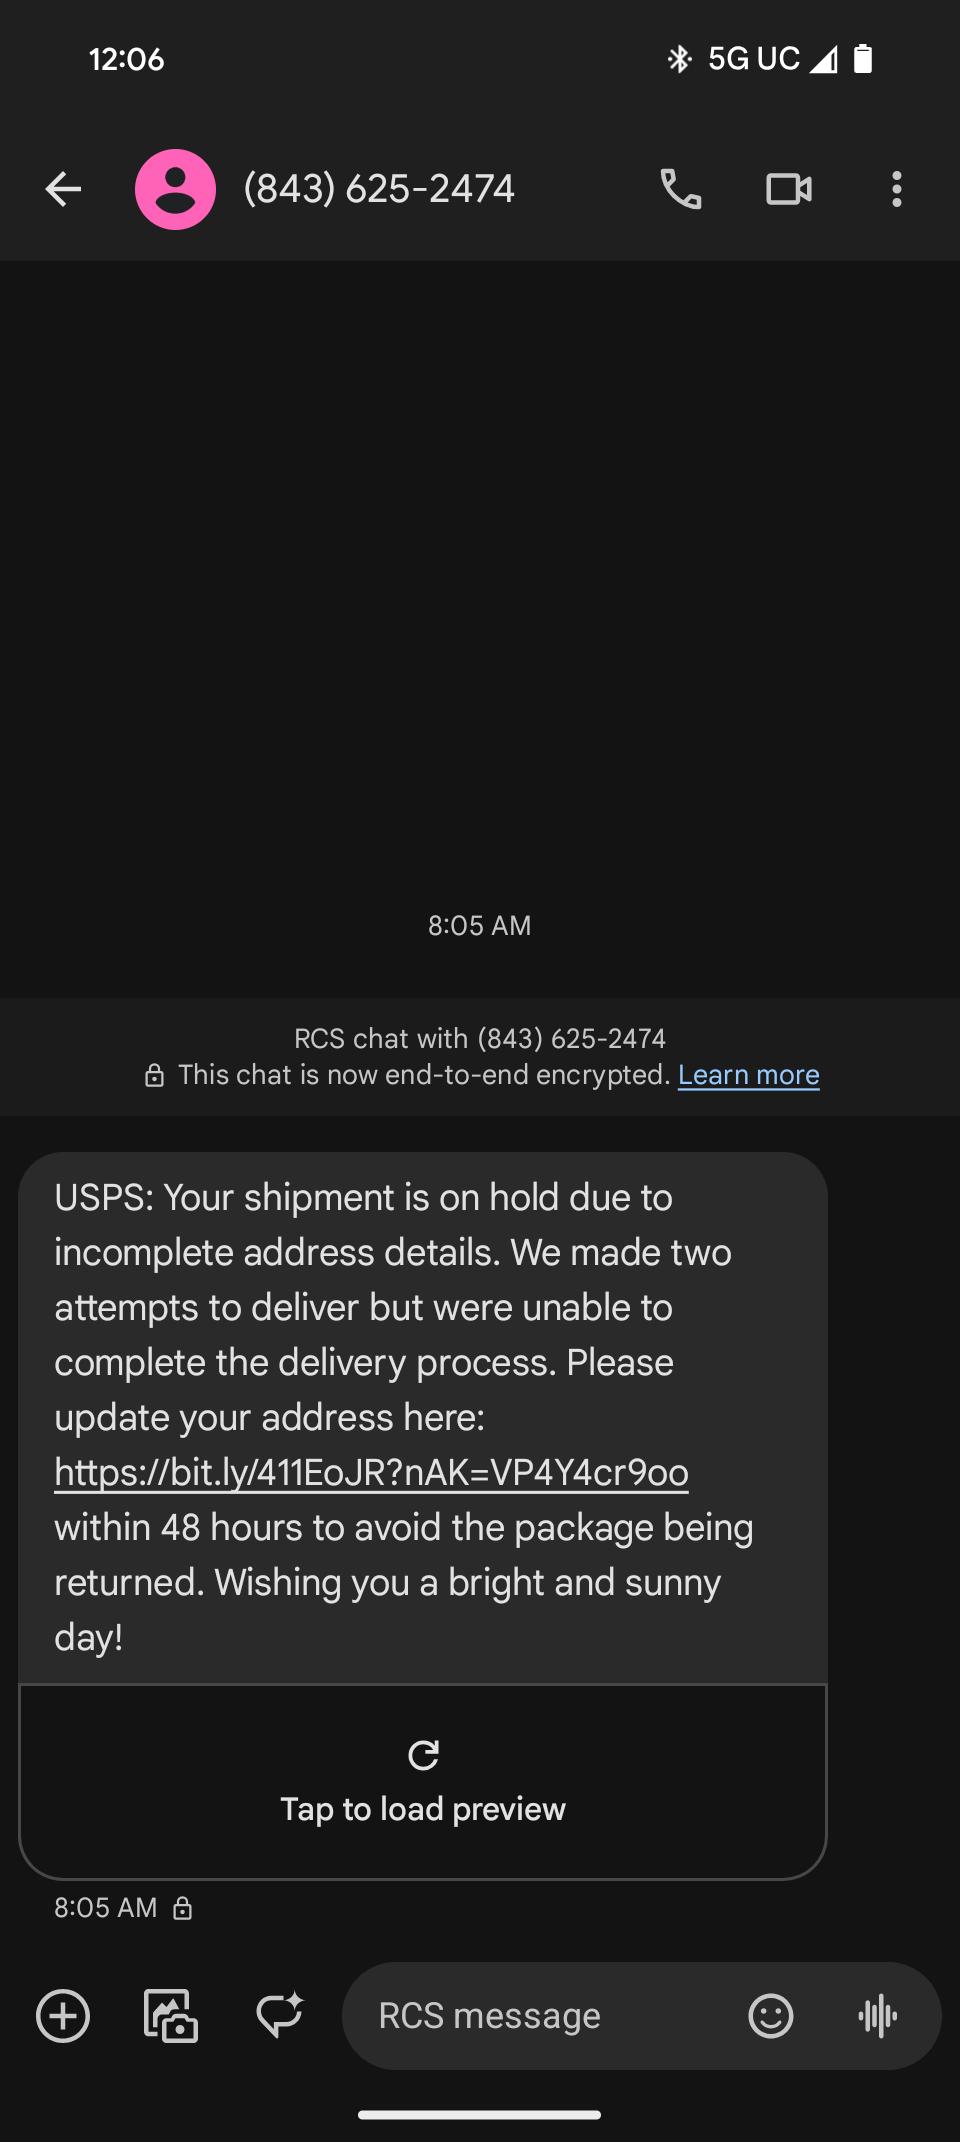
“Wishing you a bright and sunny day!” Lol, I almost want to help this guy by explaining that UPS and American companies in general have disdain for their customers and would never wish them to have anything that would not benefit the company.
You must log in or register to comment.
An official company is not going to use an URL shortener.
That’s only used when you try to hide the URL, or if you think the user is going to type it out manually.
I seriously doubt USPS bought a domain like gflrml dot cyou for their business. It’s 300% a scam.
Reminds me of my previous bank.
They changed some system countrywide, so I got an email that I need to update some data and go to a website to do that.
If was something like “update-[bankname]-data-now.tld”.
It was sent to a unique mail address I used for them. But still though it was phishing.
Turns out: No. It was real. Whoever came up with the idea to not host that stuff on at least a subdomain of the bank really needs to get fired. and each and every manager who was part of the decision process.
Had that happen, too. We all try to educate users to NOT click on some dubious phishing/scams and put in qute some effort to explain it over and over again, and then there are companies doing things like that. It’s just sad.
lol I have to go back to the bank (when there’s a manager, because there wasn’t last time🤦♀️), to turn online banking back on for my account.
It got turned off because I didn’t pick up some spam call they made.
Ugh. I work in the public sector and let me tell you, there are SO many companies that send the most dogiest, scammiest looking emails telling you to follow a link, only for it to turn out to be perfectly legitimate.
I honestly can see now why people end up falling for these things when even legitimate companies send emails looking just like phishing scammers
Also, is it common for a legitimate government agency to use a third-party link shortener like bitly?
You mean (uint32_t)-1 %
The text message is the big red flag, that’s obviously a scam and has been happening for at least a year. Most scam texts are filtered on my phone, but a few of these slip thru.
I guess they’re just trying to tie phone numbers to addresses so they can sell the phone list for more info.
Especially with people keeping their cell number while moving states, tying an address to the number and verifying it’s that person would be a tidy profit.
Link shortener (not their own at least) is another massive red flag, same with typos (‘number number’ in page)
Unfortunately I can think of one company in particular that uses tinyurl when you sign up for shipping updates on their website (looking at you Samsung!).
At least with that one:
- you know you signed up for it
- they send a text right when you sign up for it
- they use an official short SMS (5 digit) number.
Bruh, just look at the address bar. That is not a USPS domain. Obviously it’s a scam.
100% scam
Go to the official UPS website (do not click that link, google it) and enter your tracking number.
If you don’t have a tracking number it means you didn’t order anything, and it’s certainly a scam.This is usps, not ups, but everything else is accurate.
Always check the real site without using a link to get there.
I get these scam texts all the time. It’s 100% a scam, and now that you’ve clicked it, you’ll probably get a bunch more scam in the near future, so be extra cautious.
flip the question around: Why would you think this wasn’t a scam?
Furthermore, wtf did they GO TO THE URL FROM A TEXT MESSAGE at all?! 🤦🏽♂️
FFS, people. There’s “I need help with my computer” and then there’s “Some of us shouldn’t have a smartphone”. 🫶🏼
tbf, it could be sandboxed and safe. I doubt it is, OP doesn’t seem the type, but it could be.
Doesn’t matter, there’s more than likely a callback in the url that says who it was, and now the sender knows the number is active and the user clicks on links
Holding up a giant sign that says “I CLICK ON WHATEVER BULLSHIT LINK YOU SEND ME”
It’s a scam. You can tell because you’re getting it via a rcs text. I’ve never once seen a business use an encrypted text.
Also the URL of course.
Edit: nvm just discovered some doctors offices do indeed use encrypted protocols for SMS. So the text being RCS isn’t inherently suspicious. Businesses may use it. But obviously the URL gives away that it’s a scam.
You can tell because it’s a text message.
The USPS will leave you a notice in your mailbox, not text you.
Your phone number isn’t part of the address someone mails to.
Just write in the nearest Subway/McDonald’s address.
This is 10000% a scam. That’s not the USPS url scheme. Plus, as a government entity, they’ll start correspondence through certified mail. Another question you could ask yourself is “Did I order any packages lately?” IF not, then more proof it’s a scam.
I get emails from usps all the time, they have a service to alert you of mail and packages arriving. Though, they dont SMS, and wouldnt be using a bit.ly url.
You got several good answers already.
First of all, if you aren’t expecting any shipment from USPS, then why would you be updating your address details for them at all?
But even if you are: gflmr.cyou is certainly not the USPS and I highly doubt they would have errors like “package number number” and weird grammar like “because … is not clear, your package is not delivered” on their tracking website.
Yes
I think there’s now a generation gap between kids today and people who were routinely sent to tubgirl and goatse during the internet’s formal years.
If your URL is fucky, it’s a scam. If you clicked one, they’ll send you more.
Our parents couldn’t use computers properly, and now our kids can’t use them properly either.
That being said, I learned the hard way back in the golden age many, many times.
If you want to be extra sure, just contact USPS directly.
ITT things that make my chest tighten painfully