
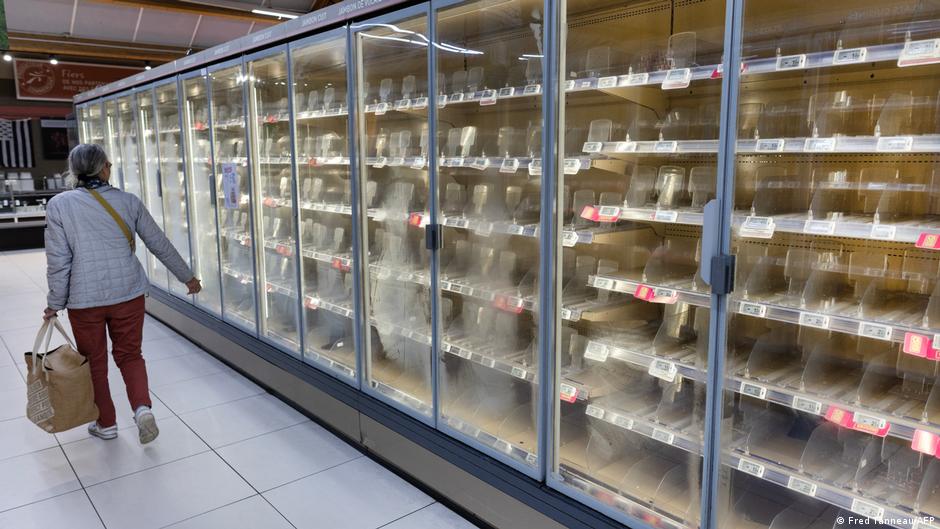
Hundreds of French supermarkets saw their refrigeration systems defrosted, spoiling tons of frozen food. The unprecedented attack has raised serious questions about food security across Europe.
Hundreds of French supermarkets were forced to throw away perishable goods on Monday after hackers commandeered refrigeration systems across the country, spoiling stock at major chains in a sophisticated overnight cyberattack.
Hackers destroyed the food by taking control of refrigeration systems at Cooperative U, Leclerc, Les Mousquetaires, and Intermarche stores across the country and then defrosting thousands of freezer and refrigeration units.
During the overnight attack, in some cases, fully-stocked fridges were heated up to 50 degrees Celsius (122 degrees Fahrenheit) for more than six hours. Over 400 stores were hit according to retailers.
Why does a supermarket refrigerator need to be able to be controlled online? Surely the day-to-day temperatures are identical year-round? I can understand the need to report temperatures, but why can they be remotely controlled at all?
I work with these controllers. Remote access is a lifesaver, makes remote diagnosis much easier, and lets us tell the client to move product before it spoils. Similar refrigeration controllera have had remote capability since the dial-up era, this isn’t a new trend.
With that said, these things need to be behind a VPN. I don’t care if the manufacturer promises their controller is safe for direct access from the internet.
It’s kinda like a factory assembly line, once these things get installed and the system is stable, the client gets allergic to any changes. I come across old control systems that have been running for 30+ years, once it’s in it’s in.
On the French news they reported that the devices affected were older and not getting security updates also that the company was foreign owned and operated.
I haven’t really seen that elsewhere, but you’re right about these obscure/old controllers becoming sacrosanct.
Probably for telemetry and monitoring
They could still broadcast their temperature (securely, hopefully), without allowing any incomming commands.
Capitalism fucks up human brains or something because you’re 100% correct and every normal engineer would agree with you. 🤷♂️
Honestly, as someone who works in an adjacent industry, anything with a thermostat inevitably gets set to a crazy value. You need something smart enough you can program it to return to normal operation after a certain amount of time.
In theory, you can get that level of control locally with a fully isolated monitoring system, but it seems silly and an unnecessary cost to have two separate systems… Until you lose your entire fridge stock to a dweeb armed with ChatGPT.
Assuming they got a PLC controlling those fridges (or, to be fair, any kind of “smart” system), can anyone explain me why the hell were they exposed to the internet?
I understand the need for them to be controlled and programmed remotely, but like… you can just have them on an internal network not exposed to the internet? I’m not gonna defend hackers because wasting food is shitty but this was a disaster waiting to happen.
Laziness and/or convenience. It’s always those. What supermarket would pay for an actual IT person that can setup a VPN and configure access control when “it just works” anyway.
It also acts as a reminder that this is also true for some critical infrastructure. Thankfully not all of them, but there’s been stories.
Probably step 5 of the quick start guide:
“It’s important that you connect your refrigerator to your WiFi to find out about incredible deals, product updates, and maybe once in a great while security patches!”
Who benefits from destroying supermarket products?
Isn’t France going through protests at the moment? Destroying the food supply adds pressure, I don’t know enough to guess who did what.
Some big org or state actor for an attack with that dimension and target. Possibly state sponsored for political pressure or but much less likely a competing business. But they usually have less obvious ways to fight competitors. So I go with a state sponsored cyber attack.
Same country, or a friend, that was trying to sabotage the Paris Olympics and paid guys to set rail infrastructure on fire to cause chaos.
What horrible people.
True, but that’s still no reason to hack their supermarkets.
i would like to know how the fuck some of them fridges got to be 50 °C. are they run on heat pumps and you can just crank them to whatever temperature with the software!? are they general purpose laboratory incubators!??!
Defrost mode. https://www.bbc.com/news/articles/crq5nzxv9q4yo
Normally, supermarket freezers go through a short period of defrosting overnight, in which temperatures rise slightly. But the hackers ordered the units to heat up and stay hot, although Danfoss did not confirm any reports about just how warm the fridges and freezers could become in that process.
Industrial controls are terrifying in terms of just how catastrophically they can cause the device to fail. Connecting machines to the internet is an incredible liability.
I once tried to beg the SCADA department to let me have a single line of sight radio transmitter for data collection. Not for control, and not even over the internet! They said no, which was the right thing to do.
Automation engineer here:
Yup, this. My cybersecurity plan for the fridges would be “what the fuck why are they exposed to any external networks for any reason?”