Share this.
is this seriously it? 26 people are supposed to know enough about the inner workings of all these departments to be able to fire staff?
there is not even an attempt to appear competent
Therewasntanattempt
Employee Relations Manager 71 At Waffle House Office Explains Odd Passion: Golf On Venus
Annnnnd I’ll just save this photo.

Might as well spam a bit to panic any crawling bots by the numbers it’s posted
I’m new around these parts. First post, here goes:

Yeah why not. I sure hope they have OCR enabled

What’s OCR? Please elaborate. I could Google it, but a personal touch is always nice.

OCR is an automation tool designed to pull text out of images or PDFs. It’s super useful, you can scan documents and then use OCR to create a markdown/plaintext copy that’s easier to search for. I like doing this for documents where I need the wording more than the paper itself, like my lease
Ah. So it’s the tech/protocol/[correctlabel] that’s behind the technology that allows me to just hold down the home button on my Samsung S24 while looking at that picture so I can just paint and copypaste this from the image?
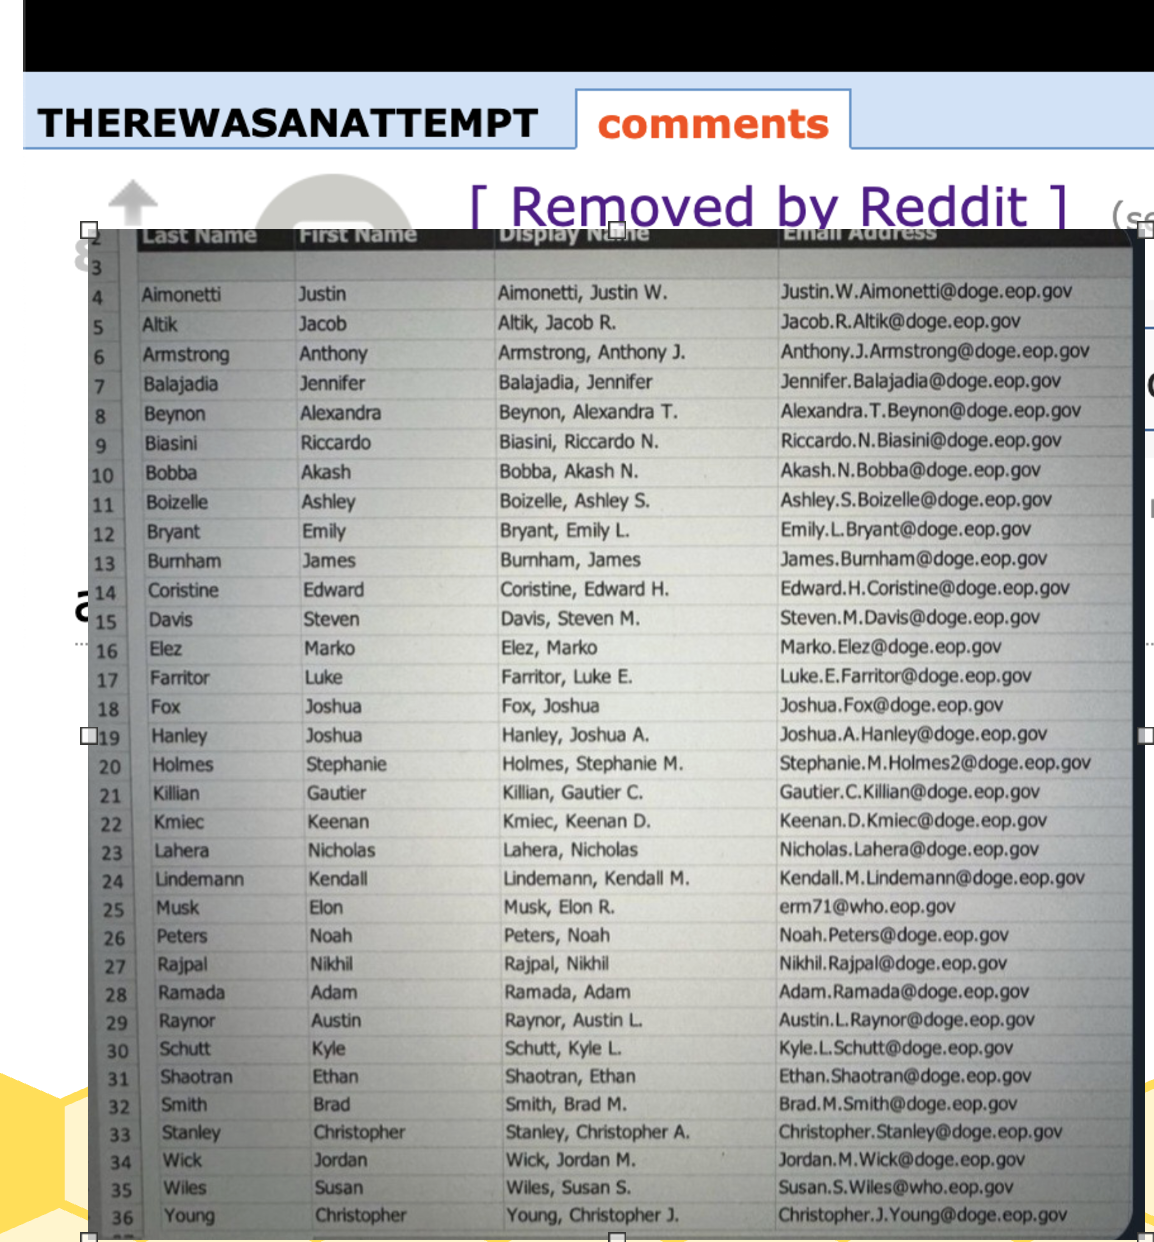
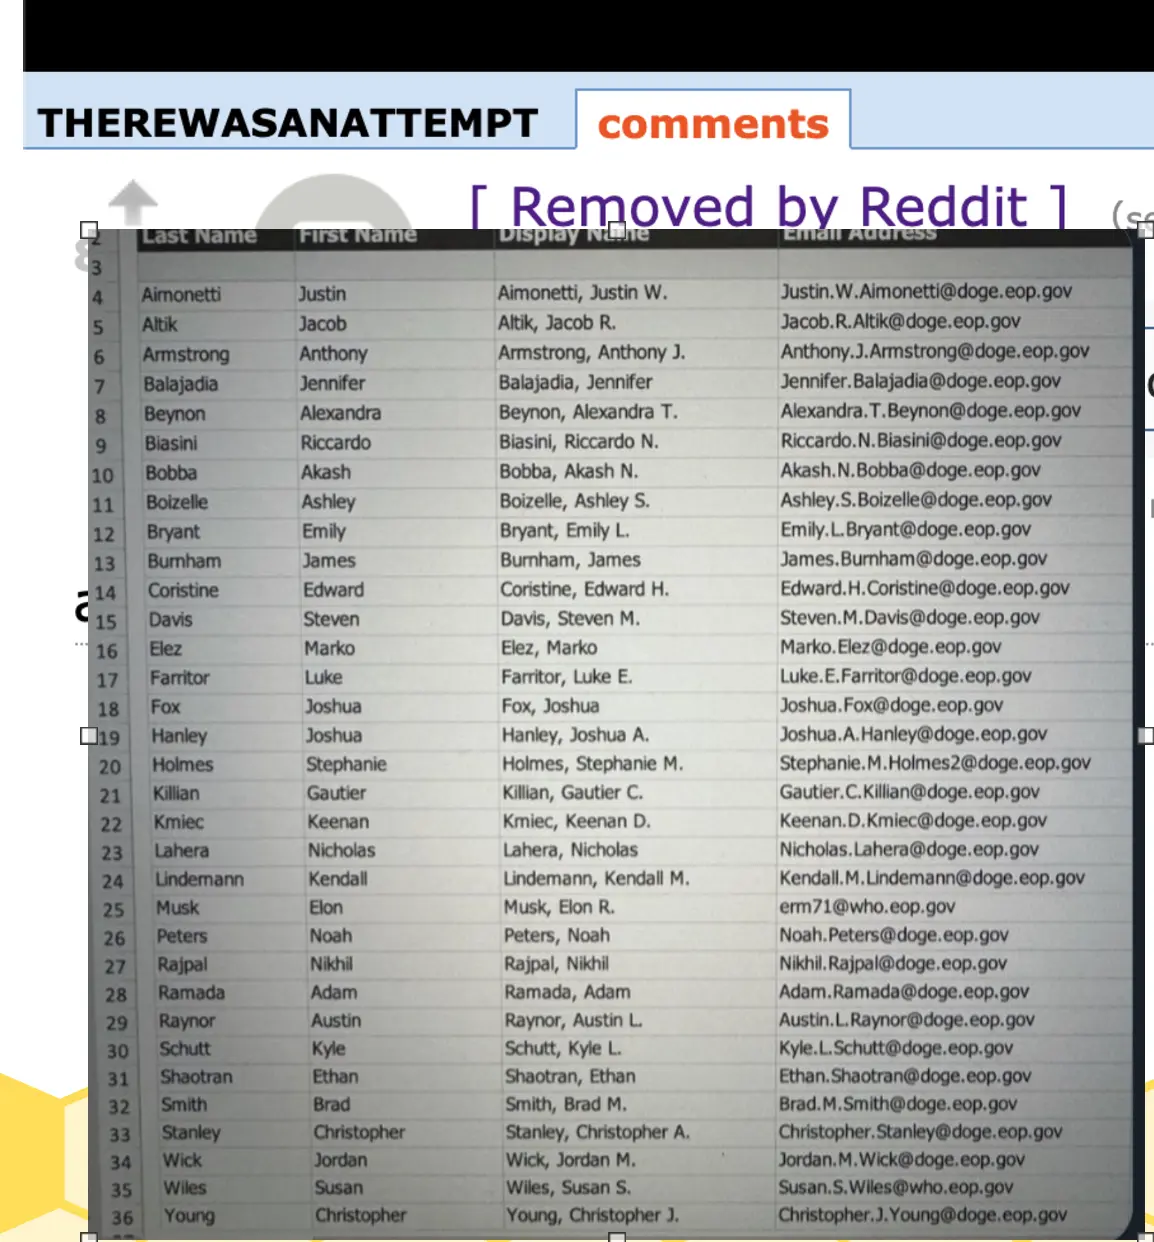
Aimonetti Altik Armstrong Balajadia Beynon Biasini Bobba Boizelle Bryant Burnham Coristine 16 17 Jacob Anthony Jennifer Alexandra Riccardo Akash Ashley Emily James Edward Steven Marko Luke 18 Davis Elez Farritor Fox Hanley 19 20 Holmes 21 Killian 22 Kmiec Lahera Lindemann Musk Joshua Joshua Stephanie Gautier Keenan Nicholas Kendall Elon Noah Nikhil Adam Austin 23 24 25 26 Peters 27 Rajpal 28 Ramada 29 30 31 Shaotran 32 33 34 35 Raynor Schutt Smith Stanley Wick Wiles 36 Young Kyle Ethan Brad Christopher Jordan Susan Christopher Removed by Reddit 1 Display Nne Aimonetti, Justin W. Altik, Jacob R. Armstrong, Anthony J. Balajadia, Jennifer Beynon, Alexandra T. Biasini, Riccardo N. Bobba, Akash N. Boizelle, Ashley S. Bryant, Emily L. Burnham, James Coristine, Edward H. Davis, Steven M. Elez, Marko Farritor, Luke E. Fox, Joshua Hanley, Joshua A. Holmes, Stephanie M. Killian, Gautier C. Kmiec, Keenan D. Lahera, Nicholas Lindemann, Kendall M. Musk, Elon R. Peters, Noah Rajpal, Nikhil Ramada, Adam Raynor, Austin L. Schutt, Kyle L. Shaotran, Ethan Smith, Brad M. Stanley, Christopher A. Wick, Jordan M. Wiles, Susan S. Young, Christopher J. Justin.W.Aimonetti@doge.eop.gov Jacob.R.Altik@doge.eop.gov Anthony.J.Armstrong@doge.eop.gov Jennifer.Balajadia@doge.eop.gov Alexandra.T.Beynon@doge.eop.gov Riccardo.N.Biasini@doge.eop.gov Akash.N.Bobba@doge.eop.gov Ashley.S.Boizelle@doge.eop.gov Emily.L. Bryant@doge.eop.gov James.Burnham@doge.eop.gov Edward.H.Coristine@doge.eop.gov Steven.M.Davis@doge.eop.gov Marko.Elez@doge.eop.gov Luke.E.Farritor@doge.eop.gov Joshua.Fox@doge.eop.gov Joshua.A.Hanley@doge.eop.gov Stephanie.M.Holmes2@doge.eop.gov Gautier.C.Killian@doge.eop.gov Keenan.D.Kmiec@doge.eop.gov Nicholas.Lahera@doge.eop.gov Kendall.M.Lindemann@doge.eop.gov erm71@who.eop.gov Noah.Peters@doge.eop.gov Nikhil. Rajpal@doge.eop.gov Adam.Ramada@doge.eop.gov Austin.L. Raynor@doge.eop.gov Kyle.L.Schutt@doge.eop.gov Ethan.Shaotran@doge.eop.gov Brad.M.Smith@doge.eop.gov Jordan.M.Wick@doge.eop.gov Susan.S.Wiles@who.eop.gov Christopher. Stanley@doge.eop.gov Christopher.).Young@doge.eop.gov
This here?

Formatted:
Last Name,First Name,Display Name,Email Address
Aimonetti,Justin,Aimonetti, Justin W.,Justin.W.Aimonetti@doge.eop.gov
Atik,Jacob,Atik, Jacob R.,Jacob.R.Atik@doge.eop.gov
Armstrong,Anthony,Armstrong, Anthony J.,Anthony.J.Armstrong@doge.eop.gov
Balajadia,Jennifer,Balajadia, Jennifer,Jennifer.Balajadia@doge.eop.gov
Beynon,Alexandra,Beynon, Alexandra T.,Alexandra.T.Beynon@doge.eop.gov
Biasini,Riccardo,Biasini, Riccardo N.,Riccardo.N.Biasini@doge.eop.gov
Bobba,Akash,Bobba, Akash N.,Akash.N.Bobba@doge.eop.gov
Boizelle,Ashley,Boizelle, Ashley S.,Ashley.S.Boizelle@doge.eop.gov
Bryant,Emily,Bryant, Emily L.,Emily.L.Bryant@doge.eop.gov
Burnham,James,Burnham, James,James.Burnham@doge.eop.gov
Coristine,Edward,Coristine, Edward H.,Edward.H.Coristine@doge.eop.gov
Davis,Steven,Davis, Steven M.,Steven.M.Davis@doge.eop.gov
Elez,Marko,Elez, Marko,Marko.Elez@doge.eop.gov
Farritor,Luke,Farritor, Luke E.,Luke.E.Farritor@doge.eop.gov
Fox,Joshua,Fox, Joshua,Joshua.Fox@doge.eop.gov
Hanley,Joshua,Hanley, Joshua A.,Joshua.A.Hanley@doge.eop.gov
Holmes,Stephanie,Holmes, Stephanie M.,Stephanie.M.Holmes@doge.eop.gov
Killian,Gautier,Killian, Gautier C.,Gautier.C.Killian@doge.eop.gov
Kmiec,Keenan,Kmiec, Keenan D.,Keenan.D.Kmiec@doge.eop.gov
Lahera,Nicholas,Lahera, Nicholas,Nicholas.Lahera@doge.eop.gov
Lindemann,Kendall,Lindemann, Kendall M.,Kendall.M.Lindemann@doge.eop.gov
Musk,Elon,Musk, Elon R.,em7m@who.eop.gov
Peters,Noah,Peters, Noah,Noah.Peters@doge.eop.gov
Rajpal,Nikhil,Rajpal, Nikhil,Nikhil.Rajpal@doge.eop.gov
Ramada,Adam,Ramada, Adam,Adam.Ramada@doge.eop.gov
Raynor,Austin,Raynor, Austin L.,Austin.L.Raynor@doge.eop.gov
Schutt,Kyle,Schutt, Kyle L.,Kyle.L.Schutt@doge.eop.gov
Shaotran,Ethan,Shaotran, Ethan,Ethan.Shaotran@doge.eop.gov
Smith,Brad,Smith, Brad M.,Brad.M.Smith@doge.eop.gov
Stanley,Christopher,Stanley, Christopher,Christopher.Stanley@doge.eop.gov
Wick,Jordan,Wick, Jordan M.,Jordan.M.Wick@doge.eop.gov
Wiles,Susan,Wiles, Susan S.,Susan.S.Wiles@doge.eop.gov
Young,Christopher,Young, Christopher J.,Christopher.J.Young@doge.eop.gov
Oh yeah. That looks good even on PC.
That looks pretty good, and yes that is an accurate finding about your phones feature. We can take this one step further though, if you can find a good webp to pdf converter like Sterling-pdf (self-host able but I don’t have a machine with me at work to do this rn), then you can convert the PDF to markdown and it will preserve the formatting. Then we can convert it to HTML and we’ve reverse engineered the page in the image and could even publish it onto the open web!
Edit: actually you can probably skip the markdown step now that I think about it lol
I mean.
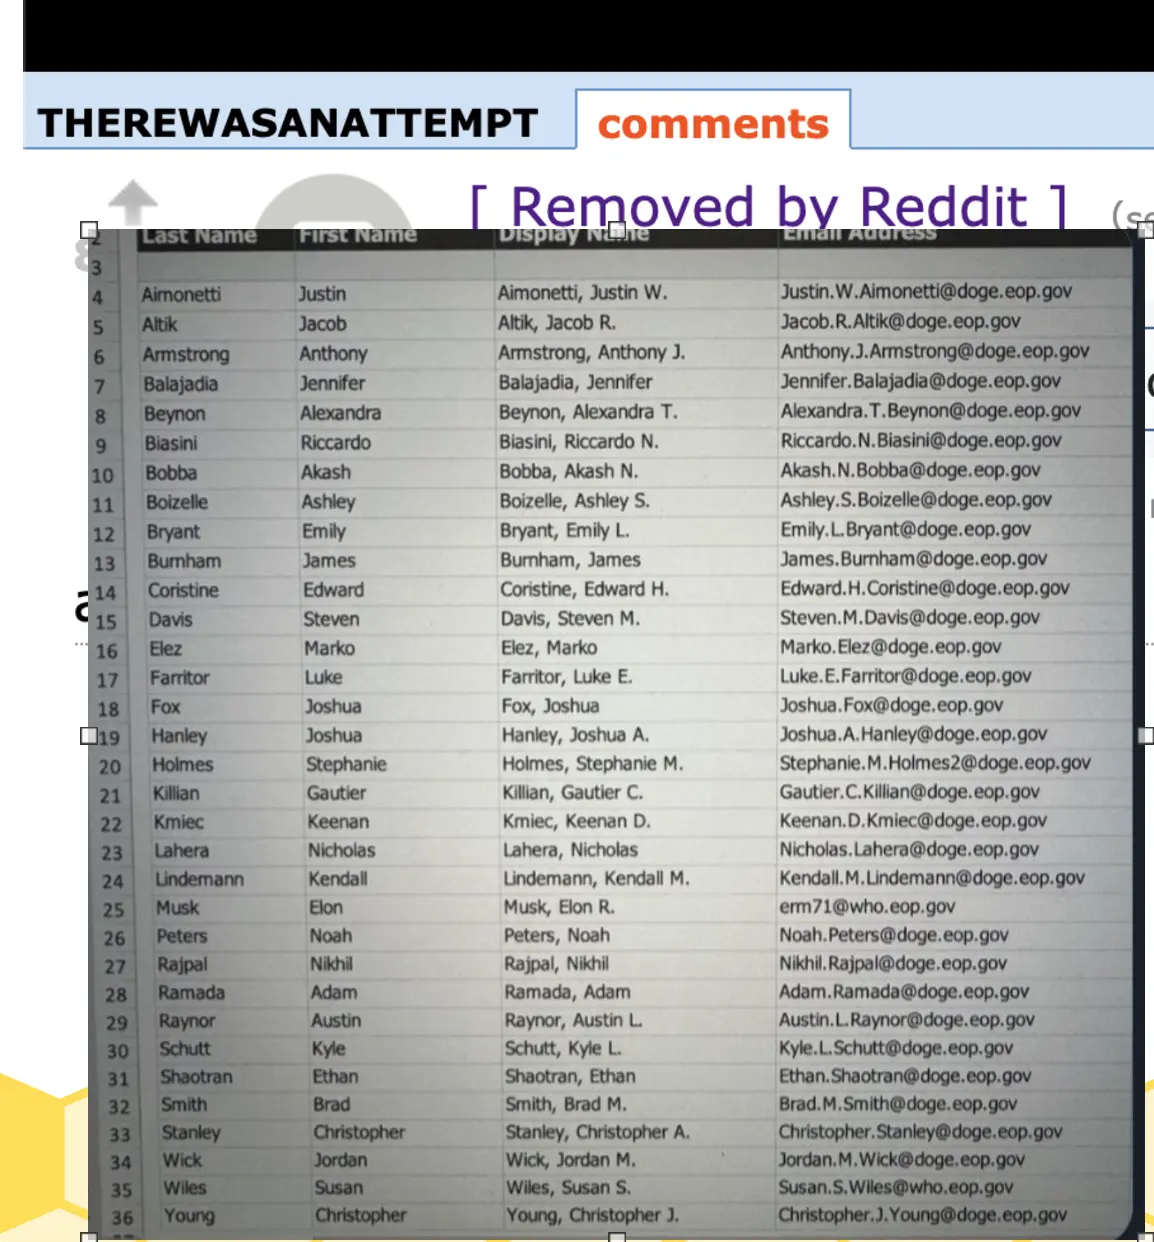
HEREWASANATTEMPT Last Name First Name Justin comments 10 Aimonetti Altik Armstrong Balajadia Beynon Biasini Bobba Boizelle 11 12 Bryant 13 Burmham 15 16 Jacob Anthony Jennifer Alexandra Riccardo Akash Ashley Emily James Edward Steven Marko Luke Joshua Coristine Davis Elez Farritor Fox Hanley Kmiec 17 18 19 20 Holmes 21 Killian 22 23 Lahera 24 25 26 27 28 29 30 31 Lindemann Musk Peters Rajpal Ramada Raynor Schutt Shaotran Joshua Stephanie Gautier Keenan Nicholas Kendall Elon Noah Nikhil Adam Austin Kyle Ethan 32 Smith 33 34 35 36 Stanley Wick Wiles Young Brad Christopher Jordan Susan Christopher Aimonetti, Justin W. Altik, Jacob R. Balajadia, Jennifer Beynon, Alexandra T. Biasini, Riccardo N. Removed by Reddit 1 Display N Armstrong, Anthony J. Bobba, Akash N. Boizelle, Ashley S. Bryant, Emily L. Burnham, James Coristine, Edward H. Davis, Steven Elez, Marko Farritor, Luke Fox, Joshua Hanley, Joshua A. Holmes, Stephanie Killian, Gautier C. Kmiec, Keenan D. Lahera, Nicholas Lindemann, Kendall M. Musk, Elon R. Peters, Noah Rajpal, Nikhil Ramada, Adam Raynor, Austin L. Schutt, Kyle L. Shaotran, Ethan Smith, Brad M. Stanley, Christopher A Wick, Jordan M. Wiles, Susan S. Young, Christopher Justin.W.Aimonetti@doge.eop.gov Jacob.R.Altik@doge.eop.gov Anthony.J.Armstrong@doge.eop.gov Jennifer. Balajadia@doge.eop.gov Alexandra.T.Beynon@doge.eop.gov Riccardo.N.Biasini@doge.eop.gov Akash.N.Bobba@doge.eop.gov Ashley.S.Boizelle@doge.eop.gov Emily.L.Bryant@doge.eop.gov James.Burnham@doge.eop.gov Edward.H.Coristine@doge.eop.gov Steven.M.Davis@doge.eop.gov Marko.Elez@doge.eop.gov Luke.E.Farritor@doge.eop.gov Joshua.Fox@doge.eop.gov Joshua.A.Hanley@doge.eop.gov Stephanie.M.Holmes2@doge.eop.gov Gautier.C.Killian@doge.eop.gov Keenan.D.Kmiec@doge.eop.gov Nicholas.Lahera@doge.eop.gov Kendall.M.Lindemann@doge.eop.gov erm71@who.eop.gov Noah.Peters@doge.eop.gov Nikhil. Rajpal@doge.eop.gov Adam.Ramada@doge.eop.gov Austin.L. Raynor@doge.eop.gov Kyle.L.Schutt@doge.eop.gov Ethan.Shaotran@doge.eop.gov Brad.M.Smith@doge.eop.gov Christopher. Stanley@doge.eop.gov Jordan.M.Wick@doge.eop.gov Susan.S.Wiles@who.eop.gov Christopher. J.Young@doge.eop.gov
It’s not perfect, but being able to do that on anything just by pressing one button is pretty nifty imo. Convenient.
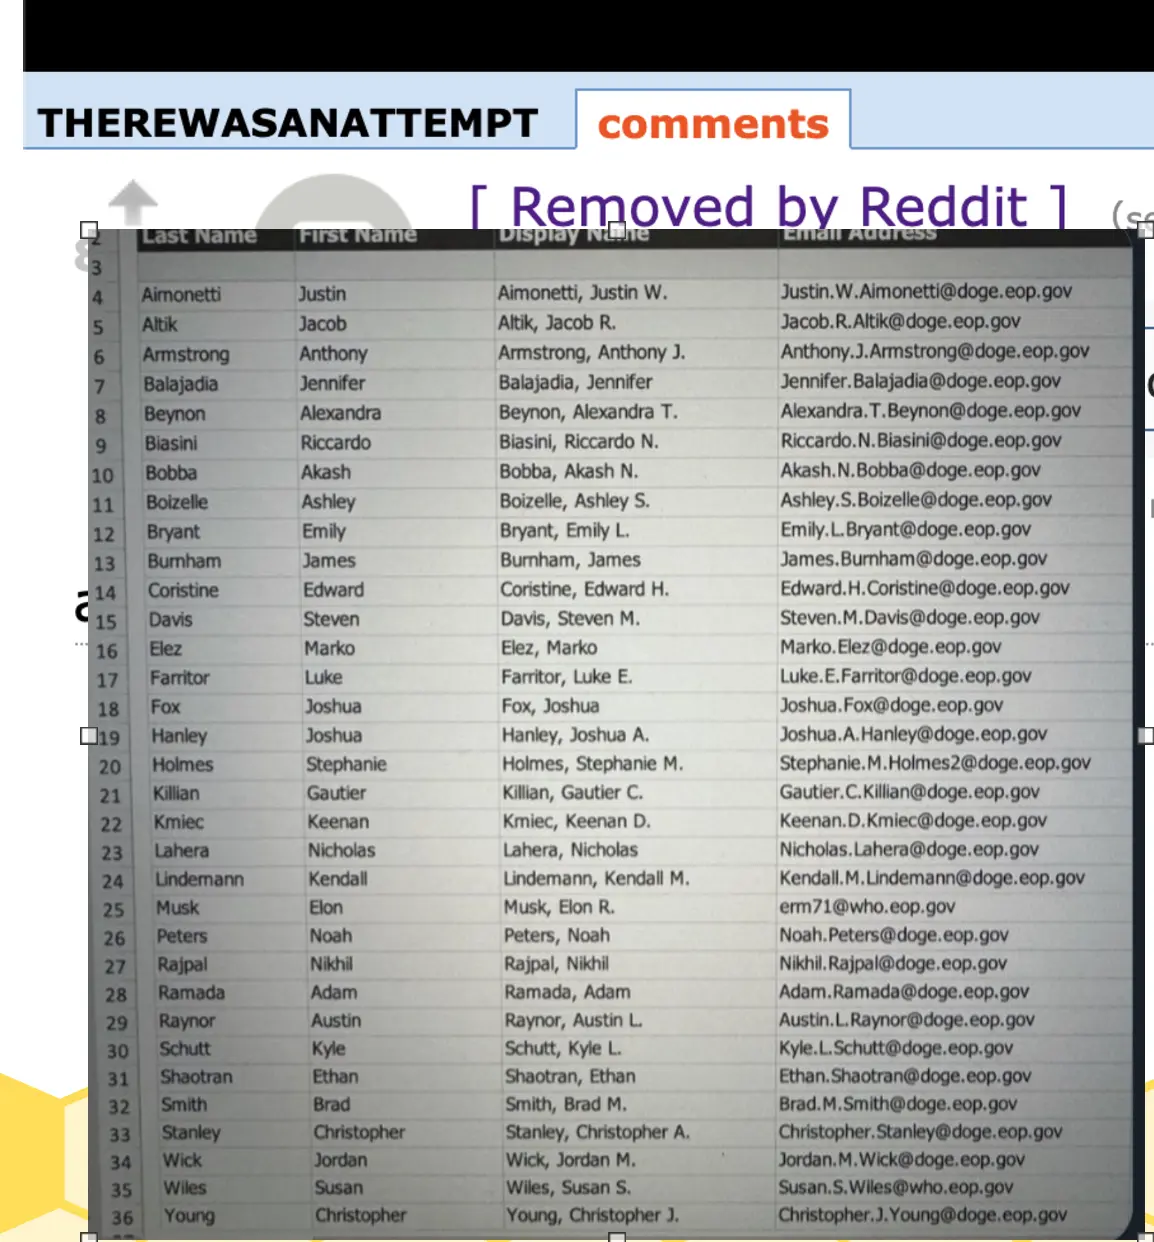
What a bunch of tools run Reddit.
It is interesting that Reddit took it upon themselves to remove it. They are government employees, those aren’t their private addresses, but end with “.gov”. This seems to be public data.
but it’s fascism time; bootlickers gonna bootlick. gotta protect the fascists from judgment by the people. expect less and less transparency moving forward, all sorts of public information getting concealed, and both mainstream media and social media corporations helping them.
The addresses were originally obtained through a Freedom of Information request, so yes, 100% public information.
Ok, so if the entire world turns into a dictatorship, with no free countries. Seriously, who will even want to live in it? How long until the population just de-pops itself?
What people want will have little to do with it, unfortunately. The “hope” is that contraception bans combined with misleading/nonexistent sex ed will maintain a population.
We’re already there?
I am 31 years old. A lot of my friends aren’t chasing partners, yet those who do don’t really want to make babies due to the long array of problems affecting quality of life.
I’m not exactly a baby-maker myself. I am quite anti-natalist as a matter of fact.
Historically, people have made babies under much more dire circumstances and some of them made it through so we’re here today. I don’t feel like having kids either, I know, but I think this sentiment comes from a luxurious position.
Despite dire circumstances those people might have had hope for the future
My mother was born in a basement during the bombardments of Dresden while the house above them was burning. Her mother had barely made it out of the second floor with burning phosphorus running down the walls. At this point, my grandparents had been on the road for quite a while, narrowly escaping the Russian front, starting with leaving behind every single thing they owned at their farm estate in Silesia. They had nothing but their clothes on their back and they already experienced, that nobody wanted anything to do with the refugees from the east.
My inconveniences are mild, compared to that. They are significant for me, but historically, we’re still at an all time high compared to our ancestors, unless you have old money in your bloodline.
Historically, people didn’t have easy access to multiple forms of birth control.
But then they’ve already started working on that: Dobbs, period policing, “NO CONDOMS FOR GAZA!!!”
Aside from the economy, the EU is pretty ok tbh…so “the whole world” is a bit of a stretch.
Central and South America as well. Canada can be fine
Funny seeing Musk on this list after his “I’m just a consultant” bit.
okay so what do you wanna do with them now?
Could be anything from on entry point on a phishing campaign to simply flooding their inbox with useless shit
Edit
Also, they likely use exchange, so if you were to spoof their email@ domain.onmicrosoft.com address, you could really trick people into thinking it was an official email from any of those addresses
These are all on the same domain. I guarantee you they have extensive spam filters in place. “Flooding their inbox” will do nothing as the messages won’t even go to their inbox.
In case you want to see some (not all) faces:
http://12ft.io/https://www.nytimes.com/interactive/2025/02/27/us/politics/doge-staff-list.html
edit: direct link: https://12ft.io/api/proxy?q=https%3A%2F%2Fwww.nytimes.com%2Finteractive%2F2025%2F02%2F27%2Fus%2Fpolitics%2Fdoge-staff-list.html
Hahaha what kinda name is that Christina Hanna 🤣
A pretty normal one?
It’s like 2 first names
Like Michael Jordan? Very weird
Hmmm, erm71… Interesting attempt to hide
To save everyone time, here’s a draft set of productivity bullets for “turtle tester”:
- Conducted thorough evaluations of turtle shell durability and structural integrity under various simulated environmental conditions.
- Monitored and recorded turtle behavior to assess mobility and adaptability in controlled habitats.
- Ensured all testing procedures adhered to ethical standards and guidelines for animal welfare.
- Collaborated with team members to analyze data and improve testing methodologies for accuracy and efficiency.
- Prepared detailed weekly reports summarizing findings and providing actionable recommendations for ongoing research.
It’s important Elon Musk knows these things.
Elon Musk strikes me as an individual who doesn’t like turtles at all. He is therefore cursed, and shall never see the light of Heaven.
Erm, what the sigma? ☝️🤓
With a quick google, what are the chances that erm71 is code for “Elon Reeve Musk 1971”.
There no way that a tech savvy individual would do something as simple as use his name and DOB for usernames and email addresses… Whats his password “teslarulez1971!”?Obviously it’s teslarulez69420!!!
And why not? You forget there is beauty in brevity.
A breach is a breach is a breach is a breach. You’d be criticizing his choice whether it was 5 simple characters or 500. When you K.I.S.S. it makes it easier to remember AND quicker to enter, access. I had to choose a password for work once, and I made it a little complex…work constantly logged me out 🙄🙄🙄🙄🙄…I had to enter that stupid fucking password so many fucking times, yes, it was secure. It was also DUMB and FRUSTRATING. Next 3 passwords were far simpler to repeatedly type in; I learned my lesson.
Same with Apple always auto-generating stupid passwords, I hope you never have to type them in! It’s just dumb, as illustrated by XKCD.
XKCD also has a suggestion for strong, memorable, easy passwords.
Be smart. Make life simple. Don’t do stupid things. 🫡
My rule: If I can’t easily write nor remember a daily password, it is crap. My strong passwords are kept in a offline password manager, which has a relatively weak master password in the vein of “R!seaboveit@ll”. Not ideal, but at least a human can type it.
The real danger is going to be websites leaking or sharing the individual password it is given. So long as no one knows your (offline) manager’s pass, the threat can be cordoned off. Unfortunately, we can expect the integration of AI into OS ecosystems to make that method vulnerable. Say, for example, Microsoft’s Copilot or Google’s Android.
Ha, son of a bitch. That is almost exactly what I do. 😆
There are always vulnerabilities; you can’t make things truly secure, you only make them less insecure.
All my passwords are longer & stronger, XKCD method, easy to read & type. Granted I don’t have Apple or my password manager generating gibberish passwords for me, takes 20 seconds each, I think them up. Maybe you should try it, too, idk. Leave the gibberish behind. I’m so glad I did.
I’m sure that is exactly what it means. The point was to hide it a little bit, it’s not the standard first.last of everyone else but to make it still uniquely identifiable as musk. It’s not a completely unheard of practice to hide potential high spam targets. The goal isn’t to completely hide, just make it slightly harder to find
This is why scraping LinkedIn works so well. Using the consistent email format gets you to your target easily. I’ve used it to get the contact info of the CTO of American Airlines before (his auto-reply included his cell number.)
That’s security through obscurity, and it doesn’t work in the long run.
No it does not. Neither does having a password as they can be leaked or cracked or who knows what. Turning off tcmp echo on your router won’t stop all bad actors but it will stop some. All security practices are just small steps to make it slightly harder for bad actors.
There is no such thing as perfect security, but there’s a big difference between trying to obscure something confidential between two parties (a password) and trying to obscure information that by design must be shared with other parties (an email address).
Outside of diligently using disposable alias addresses, obscuring an email is an exercise in futility. The biggest point of failure in security is the human, and all it takes is a single person to leak it. With all the people that need to communicate with Musk over email, the opportunity for that to happen is far higher than the chance of something like someone successfully cracking a hash.
I 100% agree with you. But I’ll also admit that I email people ALL the time and I have no idea what their email alias is. I just hit reply.
I absolutely agree with you that even with a rotation musk’s email alias will get leaked. I’m just agreeing with you that it was security through obscurification and it would have worked if one of the emails got leaked. A thousand people would have tried variations of elon.musk@ i am willing to bet none of them would have tried erm71@
And let’s face it that man has an auto forward on his email lmao
You love to see it.
Killian gautier,
Wow, sure would be a shame if someone steganographically embedded all the info into a bunch of meme images and then posted them, wouldn’t it?
[Removed by Reddit]
Of course Steve Cuckman would be the first to try and cover this up.
But which email address is for Big Balls?
If you look most are “first_name.last_name@” so it should be big.balls@doge.eop.com